PHP2Shell – What Really Happened and What Sri Lankan Businesses Should Learn
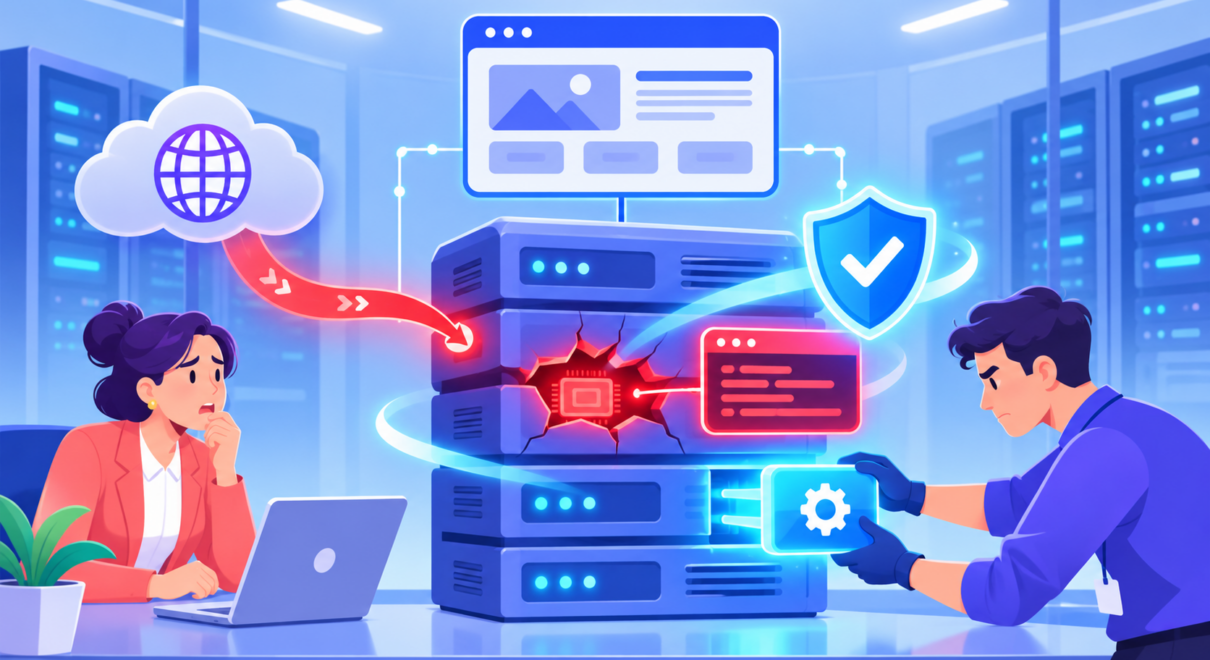
PHP2Shell is the name given to two critical PHP security vulnerabilities disclosed on 21 October 2026. The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, could allow an unauthenticated attacker to execute malicious code on a vulnerable server. This means an attacker may not need a username or password to begin an attack.
The vulnerabilities received a critical CVSS score of 9.2. The PHP Security Team released urgent security updates and advised all PHP users to upgrade immediately.
What Really Happened?
PHP is the technology behind many websites and web applications, including WordPress websites, custom business systems, e-commerce platforms and online portals. The PHP2Shell vulnerabilities affected how PHP handled memory and request information. A specially prepared web request could cause PHP to process damaged or outdated internal data.
If successfully exploited, an attacker could potentially
- Run unauthorised commands
- Install malware or a web shell
- Access sensitive website data
- Modify or delete files
- Disrupt website services
- Use the compromised server to attack other systems
This was a weakness in the PHP runtime itself, not simply a WordPress plugin problem. The official PHP advisory stated that installations using PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed could be at risk. The highest demonstrated risk was associated with mod_php because an attack could occur before the website’s application code started running.
Which PHP Versions Should Be Updated?
The PHP Security Team released the following fixed versions:
| PHP Branch | Fixed Version |
|---|---|
| PHP 8.5 | 8.5.12 or later |
| PHP 8.4 | 8.4.27 or later |
| PHP 8.3 | 8.3.36 or later |
| PHP 8.2 | 8.2.35 or later |
PHP 8.1 and older versions are no longer supported directly by the PHP project. Businesses using these versions should check whether their hosting or operating-system vendor provides a backported security fix. Otherwise, the website should be migrated to a supported PHP version. The PHP Security Team clearly stated that temporary configuration changes are not complete solutions. Installing the appropriate security update is the safest action.
Were Sri Lankan Businesses Affected?
Sri Lanka CERT issued a critical security alert for PHP-powered applications, services and products that include PHP. This means Sri Lankan organisations should take the vulnerability seriously, even if they have not noticed any visible website problems. There is no public evidence that every Sri Lankan PHP website was attacked. However, many local businesses use WordPress, custom PHP systems, shared hosting, cPanel, Plesk and older applications that may depend on outdated PHP versions.
A business may be exposed without knowing it, especially when
- The website has not been maintained regularly
- PHP updates are controlled by the hosting provider
- An older PHP version is retained for compatibility
- Server and application logs are not monitored
- Backups exist but have never been tested
- Third-party software includes its own PHP installation
- Internet-facing management panels are not properly protected
Hotels, online stores, educational institutions, healthcare providers, professional-service companies and non-profit organisations could all experience serious disruption if a website or server is compromised.
What Should Businesses Do Now?
1. Check Every PHP Installation
Identify the PHP versions used by websites, web applications, hosting panels, servers, containers and other internet-facing products. Do not assume that PHP is absent simply because the main website uses another technology. Some supporting tools may include it.
2. Apply the Security Update
Upgrade to a fixed and supported PHP version as soon as possible. Create a full backup and test the update in a safe environment when the website is business-critical.
3. Check for Signs of Compromise
Review server logs, recently modified files, administrator accounts, scheduled tasks and unusual website traffic. Installing the update prevents future exploitation of these vulnerabilities, but it does not automatically remove malware if the system was already compromised.
4. Protect Backups
Maintain separate backups of the website files and database. At least one backup should be stored outside the main hosting environment. Businesses should also test whether backups can be restored successfully.
5. Strengthen Server Security
Use appropriate firewall or WAF protection, limit access to management panels, enable multi-factor authentication and remove unused accounts, plugins and applications.
6. Introduce Ongoing Website Maintenance
Critical vulnerabilities can appear with very little warning. A website that is reviewed only when something stops working may remain exposed for weeks or months. Regular maintenance should include software updates, backups, security monitoring, malware scanning and functional testing.
How Extreme IT Solutions Can Help
Extreme IT Solutions provides website maintenance and technical support for Sri Lankan and international businesses.
Our support services can include:
- PHP version and compatibility checks
- PHP security updates and controlled upgrades
- WordPress and custom PHP maintenance
- Website malware scanning and cleanup
- Suspicious file and administrator-account reviews
- Website backup and recovery support
- Hosting, server, SSL and DNS troubleshooting
- Firewall and WAF configuration support
- Performance and security improvements
- Monthly or annual website maintenance plans
We can review the website, hosting environment and supporting services to identify outdated technology and practical security risks. No company can guarantee that a website will never experience a cyberattack. However, regular maintenance, timely updates and professional monitoring can significantly reduce avoidable exposure.
Protect Your Website Before the Next Vulnerability
PHP2Shell reminds us that website security is an ongoing responsibility. A website may look normal while outdated server technology creates a serious business risk. If you are unsure whether your website is protected, Extreme IT Solutions can complete an initial website and PHP security review.
Contact Extreme IT Solutions or email info@extremeit.lk to discuss your requirements.